Open source · MIT · v0.10.0
Find the security holes AI writes into your LLM app.
llm-audit checks TypeScript and JavaScript for the 12 mistakes behind most LLM security bugs, mapped to the OWASP LLM Top 10. Then it teaches you each one with your own code, and hands you a prompt to fix it.
npx llm-audit scan
Needs the Semgrep engine once: brew install semgrep or pipx install semgrep.
Scan
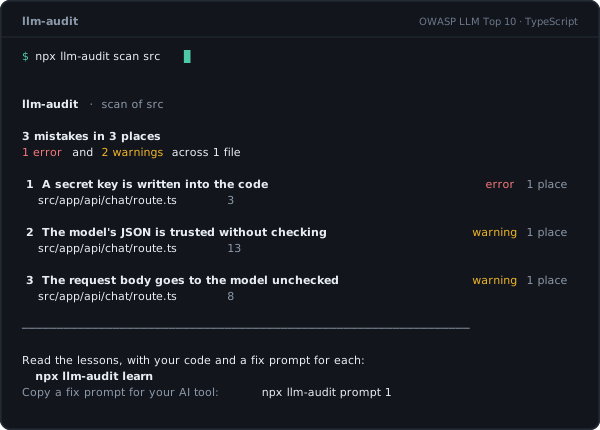
At your terminal, mistakes are grouped worst first, with every place they occur.
Learn
npx llm-audit learn opens one lesson per mistake: where it is in your code, what is going on, and how someone would use it against you.

Fix
Every lesson ends in a prompt for Claude Code, Cursor, or whatever wrote the code. It already lists each file and line to change.
npx llm-audit prompt 1
Copies lesson 1's fix prompt. Add --check for a prompt that searches the rest of the project for the same mistake.

What it catches
12 rules in 11 lessons. Each rule ships with a vulnerable example that must fire and a fixed one that must stay quiet, checked on every release.
Someone else gives your model orders
- User text is mixed into the model's instructionserrorWhoever types into your app can rewrite the rules your model follows.
- Retrieved documents are treated as instructionserrorWhoever wrote a document your app retrieves can give orders to your model.
- The request body goes to the model uncheckedwarningAnything a client sends, of any shape or size, lands in your model call.
The model's output is trusted
- Model output is run as code or HTMLerrorA string the model wrote is passed to eval, a shell, or innerHTML.
- The model's JSON is trusted without checkingwarningJSON.parse on a model reply, then the fields are used as if they were right.
- Model markdown is rendered with raw HTML onerrorHTML inside a model reply goes into the page as live HTML, so it can run scripts.
Secrets leak
- A secret key is written into the codeerrorAnyone who can read this file can spend money on your account.
- A secret is put inside the prompterrorThe model can repeat anything it was given, including your keys.
- Your system prompt ships to the browsererrorA prompt in a client component is in the JavaScript every visitor downloads.
Your code stays put
- Runs on your machine. The scan is Semgrep with llm-audit's rules, offline. No account, no upload, no telemetry.
- The lessons page is a static file. Its security policy blocks every network request. A share link carries the results after the
#, which browsers never send to a server. - Secrets are redacted in every output that shows code: terminal, JSON, HTML, and lessons.
- No dependencies. Nothing extra in your supply chain, and every release is published from CI with signed provenance.
Ready for real repos
- Pre-commit hook
- Scans only staged files.
npx llm-audit initinstalls it, with a GitHub Actions workflow. - Pull request annotations
- In GitHub Actions, findings appear on the changed lines, with a summary on the job page.
- Baseline
--baseline origin/mainreports only new findings, so you can turn the gate on today.- Ignores need a reason
// llm-audit-ignore <rule> -- <why>. Without a reason it is not applied.- One config file
.llm-audit.jsonholds the policy for the hook, CI, and your terminal.- Every format
- Versioned JSON for agents, SARIF for code scanning, a standalone HTML report.
Why not Semgrep's AI pack?
Run both. Semgrep's official p/ai-best-practices is good work, but it doesn't scan TypeScript.
| llm-audit | p/ai-best-practices | |
|---|---|---|
| JS / TS rules | 12 | 0 of 27 |
| Focus | TypeScript, TSX, JavaScript | Python, config, Bash |
| Teaches the fix | Lessons and fix prompts | Rule messages |
| Runs at | Pre-commit and CI | CI |
Start
# once
brew install semgrep

# see all twelve rules fire on bundled examples
npx llm-audit demo

# your project
npx llm-audit scan
npx llm-audit learn

# make it permanent: pre-commit hook, CI, agent skill
npx llm-audit init --skill